Item number FW-ZTNA-10G

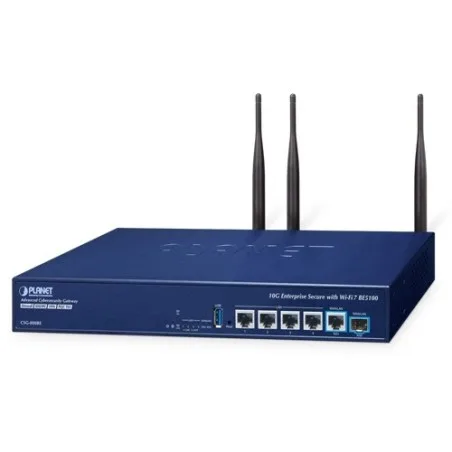
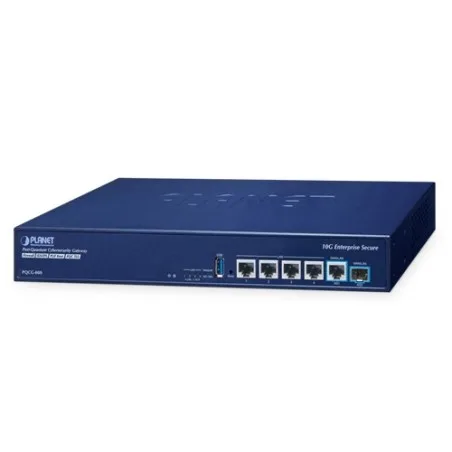
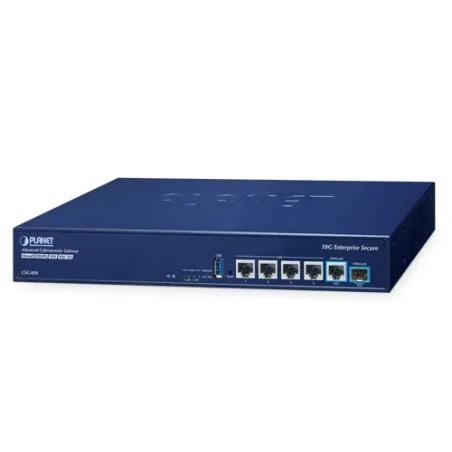
Zero Trust VPN Gateway with MFA and ZTNA, 10G RJ45 + 10G SFP+, 4 x Gigabit LAN

Zero Trust management with FIDO2 passkey, TOTP MFA and certificate login

VPN portal: users must be verified before they receive a VPN profile

ZTNA overlay: encrypted tunnels between sites without exposed services

1 x 10G RJ45 and 1 x 10G SFP+ (WAN or LAN) plus 4 x Gigabit LAN

VPN: IPsec, WireGuard, SSL (OpenVPN), L2TP, PPTP and GRE

SPI firewall with DoS/DDoS protection and web, IP and MAC filtering

Dual WAN with failover and load balancing plus high availability (HA)

Secure Boot, hardware TRNG and post-quantum TLS ready

737.00 €
Excl. VAT
Quantity
On the way in
file_download DOWNLOADS

Specifications

Operating Temp. 0 to 50 °C
Andet ZTNA overlay, VPN portal, FIDO2/TOTP MFA, Secure Boot, HA, RADIUS, captive portal, post-quantum TLS
Firewall SPI, DoS/DDoS, web/IP/MAC filtering
Porte 4 x Gigabit RJ45 (LAN), 1 x 10G RJ45 (WAN/LAN), 1 x 10G SFP+ (WAN/LAN), 1 x USB 2.0
Strømforsyning 100-240 V AC, 50/60 Hz, max. 11 W
VPN IPsec, WireGuard, SSL (OpenVPN), L2TP, PPTP, GRE. WireGuard up to 1.9 Gbps
Material Metal housing, 1U, desktop or 19" rack
WWAN Dual WAN with failover and load balancing (10G RJ45 + 10G SFP+)
Weight 1.7 kg
Dimensioner 330 x 200 x 43 mm (1U)

This Zero Trust VPN gateway is built to ensure that only verified people and devices gain access to the network and to the gateway itself. It combines FIDO2 passkeys, TOTP-based multi-factor login and certificates with fast 10G connectivity and VPN. It suits companies with several sites, remote workers and external suppliers.

Zero Trust and ZTNA

Administrators must be verified with a FIDO2 passkey, TOTP-based multi-factor login or certificate before they can change anything on the gateway. A built-in VPN portal requires users to be verified before they receive a VPN profile for OpenVPN or WireGuard, optionally via your own RADIUS server. With ZTNA overlay, verified gateways can set up encrypted tunnels directly between sites without exposing internal services to the internet. SPI firewall, DoS/DDoS protection and web, IP and MAC filtering protect the network, and Secure Boot ensures that only approved firmware can start.

Connections and VPN

The gateway has 4 x Gigabit LAN, 1 x 10G RJ45 and 1 x 10G SFP+. Both 10G ports can be used as WAN or LAN, so you can run two internet connections with automatic failover and load balancing, for example fibre and copper. The SFP+ port accepts both SFP and SFP+ modules for multimode and single-mode fibre. VPN is supported with IPsec, WireGuard, SSL (OpenVPN), L2TP, PPTP and GRE. WireGuard reaches up to 1.9 Gbps and IPsec up to 1.3 Gbps, and NAT throughput is up to 9.4 Gbps.

Operation and management

Management is via web interface, SSHv2 and SNMPv3, with dashboard and system log. The gateway supports high availability (HA), OSPF and RIP, VLAN, RADIUS, captive portal and access point management. It comes in a 1U metal housing for desktop or 19" rack, uses max. 11 W and connects to 100-240 V AC.

If you also need IDS/IPS and application control, choose one of our security gateways with IPS/IDS.